Decrypt Consumed Messages
End-to-end message encryption in Silverback is handled transparently in the producer and consumer and works independently from the used Serializing the Produced Messages or other features like Producing Chunked Messages. The consumer automatically decrypts messages if the endpoint is configured with the appropriate decryption settings.
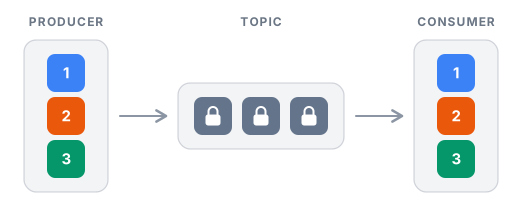
Symmetric Decryption
Enabling end-to-end decryption using a symmetric algorithm requires additional configuration on the endpoint.
The default symmetric encryption algorithm is AES.
services.AddSilverback()
    .WithConnectionToMessageBroker(options => options.AddKafka())
    .AddKafkaClients(clients => clients
        .WithBootstrapServers("PLAINTEXT://localhost:9092")
        .AddConsumer("consumer1", consumer => consumer
            .Consume<MyMessage>("endpoint1", endpoint => endpoint
                .ConsumeFrom("my-topic")
                .DecryptUsingAes(decryptionKey))));
But you can customize it.
services.AddSilverback()
    .WithConnectionToMessageBroker(options => options.AddKafka())
    .AddKafkaClients(clients => clients
        .WithBootstrapServers("PLAINTEXT://localhost:9092")
        .AddConsumer("consumer1", consumer => consumer
            .Consume<MyMessage>("endpoint1", endpoint => endpoint
                .ConsumeFrom("my-topic")
                .Decrypt(new SymmetricDecryptionSettings
                {
                    AlgorithmName = "TripleDES",
                    Key = decryptionKey
                }))));
The SymmetricDecryptionSettings class contains common algorithm settings (block size, initialization vector, ...). The AlgorithmName value is passed to SymmetricAlgorithm.Create(string). AES is used by default.
Random Initialization Vector
If the producer didn't set a static initialization vector, a random IV is generated per message and prepended to the ciphertext. The consumer automatically extracts the IV and uses it for decryption. This is the recommended behavior for improved security.
Key Rotation
To support key rotation the producer can include an identifier for the key used to encrypt each message. The consumer must be able to resolve keys by identifier to decrypt historic messages. This is done specifying a key provider function.
services.AddSilverback()
    .WithConnectionToMessageBroker(options => options.AddKafka())
    .AddKafkaClients(clients => clients
        .WithBootstrapServers("PLAINTEXT://localhost:9092")
        .AddConsumer("consumer1", consumer => consumer
            .Consume<MyMessage>("endpoint1", endpoint => endpoint
                .ConsumeFrom("my-topic")
                .DecryptUsingAes(
                    keyIdentifier => keyIdentifier switch
                    {
                        "old-key" => oldKey,
                        _ => currentKey
                    }))));
The key provider function receives the key identifier read from the message headers (null if the message doesn't specify any) and must return the key as byte[]. How the keys are stored and resolved depends on your integration.